Air-Gapped Speech Synthesis: Generating Voiceovers Without Cloud Data Leaks
Air-gapped speech synthesis is the cryptographic and operational practice of generating human-like artificial intelligence voiceovers on a physica...
Air-gapped speech synthesis is the cryptographic and operational practice of generating human-like artificial intelligence voiceovers on a physically isolated computer that has no active connection to the internet or local area network. In 2026, enterprise defense contractors, healthcare organizations, legal firms, and Hollywood production studios deploy local Windows neural TTS software like Vocal Cipher to synthesize voiceovers directly on local workstation hardware. Because all text processing, neural tokenization, and vocoder acoustic rendering execute entirely within local VRAM and system memory without transmitting packets across the web, organizations eliminate corporate espionage vulnerabilities, third-party sub-processor data leaks, and compliance violations under HIPAA, GDPR, and ITAR regulations.
In the contemporary enterprise landscape, data security boundaries are under continuous assault. The rapid adoption of cloud-hosted artificial intelligence tools has created a perilous blind spot in corporate information security: the unmonitored transmission of sensitive text prompts and internal manuscripts to remote third-party API endpoints.
When an instructional designer pastes an unannounced medical device training script into a web browser, or an entertainment editor sends an unreleased feature film script through a cloud voice generator, that intellectual property leaves the organization's fortified perimeter. It traverses public internet transit backbones, resides on shared cloud server clusters, and is frequently logged in unencrypted diagnostic telemetry databases.
This technical architecture manual outlines the threat surface of cloud speech APIs, explains the cryptographic imperatives of air-gapped synthesis, and demonstrates how organizations can achieve absolute data privacy using Vocal Cipher on isolated Windows hardware.
Vocal Cipher operates 100% offline with zero cloud telemetry, ensuring complete manuscript sovereignty.
The Cloud Data Leak Surface: What Really Happens to Your Text
Most content creators assume that using a cloud text-to-speech platform is a private transaction between their browser and a server. From an enterprise cybersecurity perspective, however, submitting text to a cloud voice API triggers an extensive chain of exposure events:
The 5 Points of Cloud Exposure
1. Ingestion Logging & Ingress Gateway Inspection
When an API request hits a cloud provider's edge gateway, standard reverse proxies (such as Cloudflare, NGINX, or AWS API Gateway) routinely log HTTP request payloads for debugging and performance profiling. Your sensitive text script is written into plaintext application logs that are accessible to junior cloud support staff and systems engineers.
2. Content Moderation & Safety Inspection Queues
To prevent platform misuse, cloud platforms route incoming text through automated safety classifiers or forward flagged snippets to third-party human review contractors. If your proprietary screenplay or defense briefing contains simulated military terms or intense dialogue, human moderators may review and inspect your confidential prose.
3. Model Training & Data Harvesting Terms
Unless an enterprise signs an expensive custom negotiated agreement, standard Terms of Service on popular cloud platforms grant the vendor perpetual rights to use input text for 'model evaluation, research, and algorithmic enhancement'. Your proprietary writing style and unpublished plotlines effectively become training data for future competitive commercial models.
4. Multi-Tenant Memory Leakage & Hypervisor Exploits
In public cloud environments, your neural inference job runs on shared GPUs alongside workloads from hundreds of other tenants. Side-channel memory attacks, VRAM residue exploits, and hypervisor vulnerabilities can allow malicious co-tenants to extract text fragments from shared memory buffers.
5. Legal Subpoenas & Extraterritorial Jurisdiction
Data stored on foreign commercial servers is subject to legal search warrants, national security letters, and cross-border discovery orders under the US CLOUD Act, bypassing your organization's domestic legal protections without your knowledge.
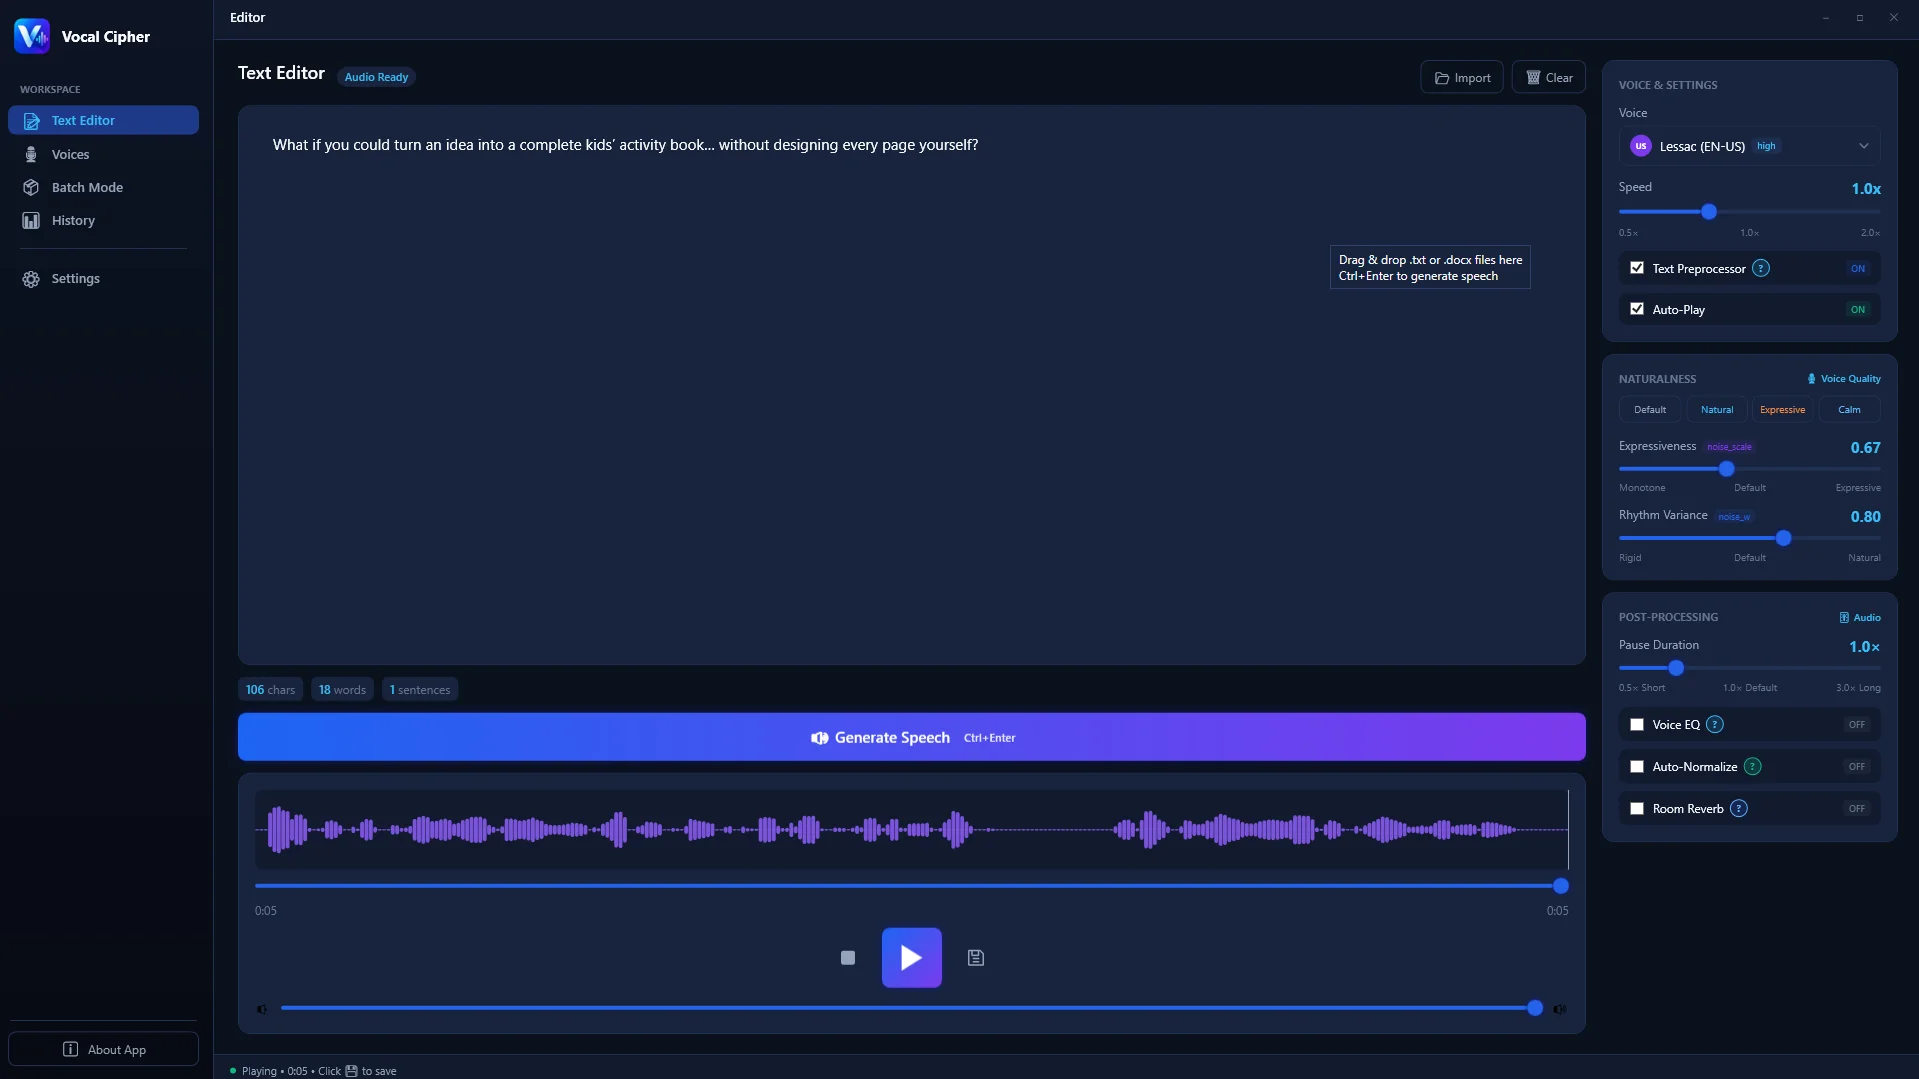
Draft, edit, and synthesize confidential manuscripts inside Vocal Cipher without transmitting packets outside your PC.
What Constitutes True Air-Gapped Speech Synthesis?
The term 'offline' is frequently abused in modern software marketing. Many desktop applications claim to be offline while secretly broadcasting background telemetry, performing hourly license heartbeats, or transmitting anonymous diagnostic pings to cloud analytics vendors.
In military and enterprise cybersecurity, a system is only recognized as genuinely air-gapped when it adheres strictly to four physical and architectural benchmarks:
The 4 Pillars of True Air-Gap Architecture
- Physical Network Severance: The host PC can operate indefinitely with the physical Ethernet cable disconnected and Wi-Fi hardware radios disabled at the BIOS/UEFI level.
- Self-Contained Local Weights: All deep learning acoustic models, text tokenizers, phonetic lexicons, and neural vocoder weights reside on the local NVMe drive. No dynamic model downloads or remote dependencies are triggered at runtime.
- Zero License Phone-Home: Software activation does not require perpetual cloud pinging. License verification occurs statically via local cryptographic key certificates.
- Absolute Telemetry Elimination: The application binary binds zero network sockets and issues zero DNS queries, crash dumps, or usage analytics over external network interfaces.
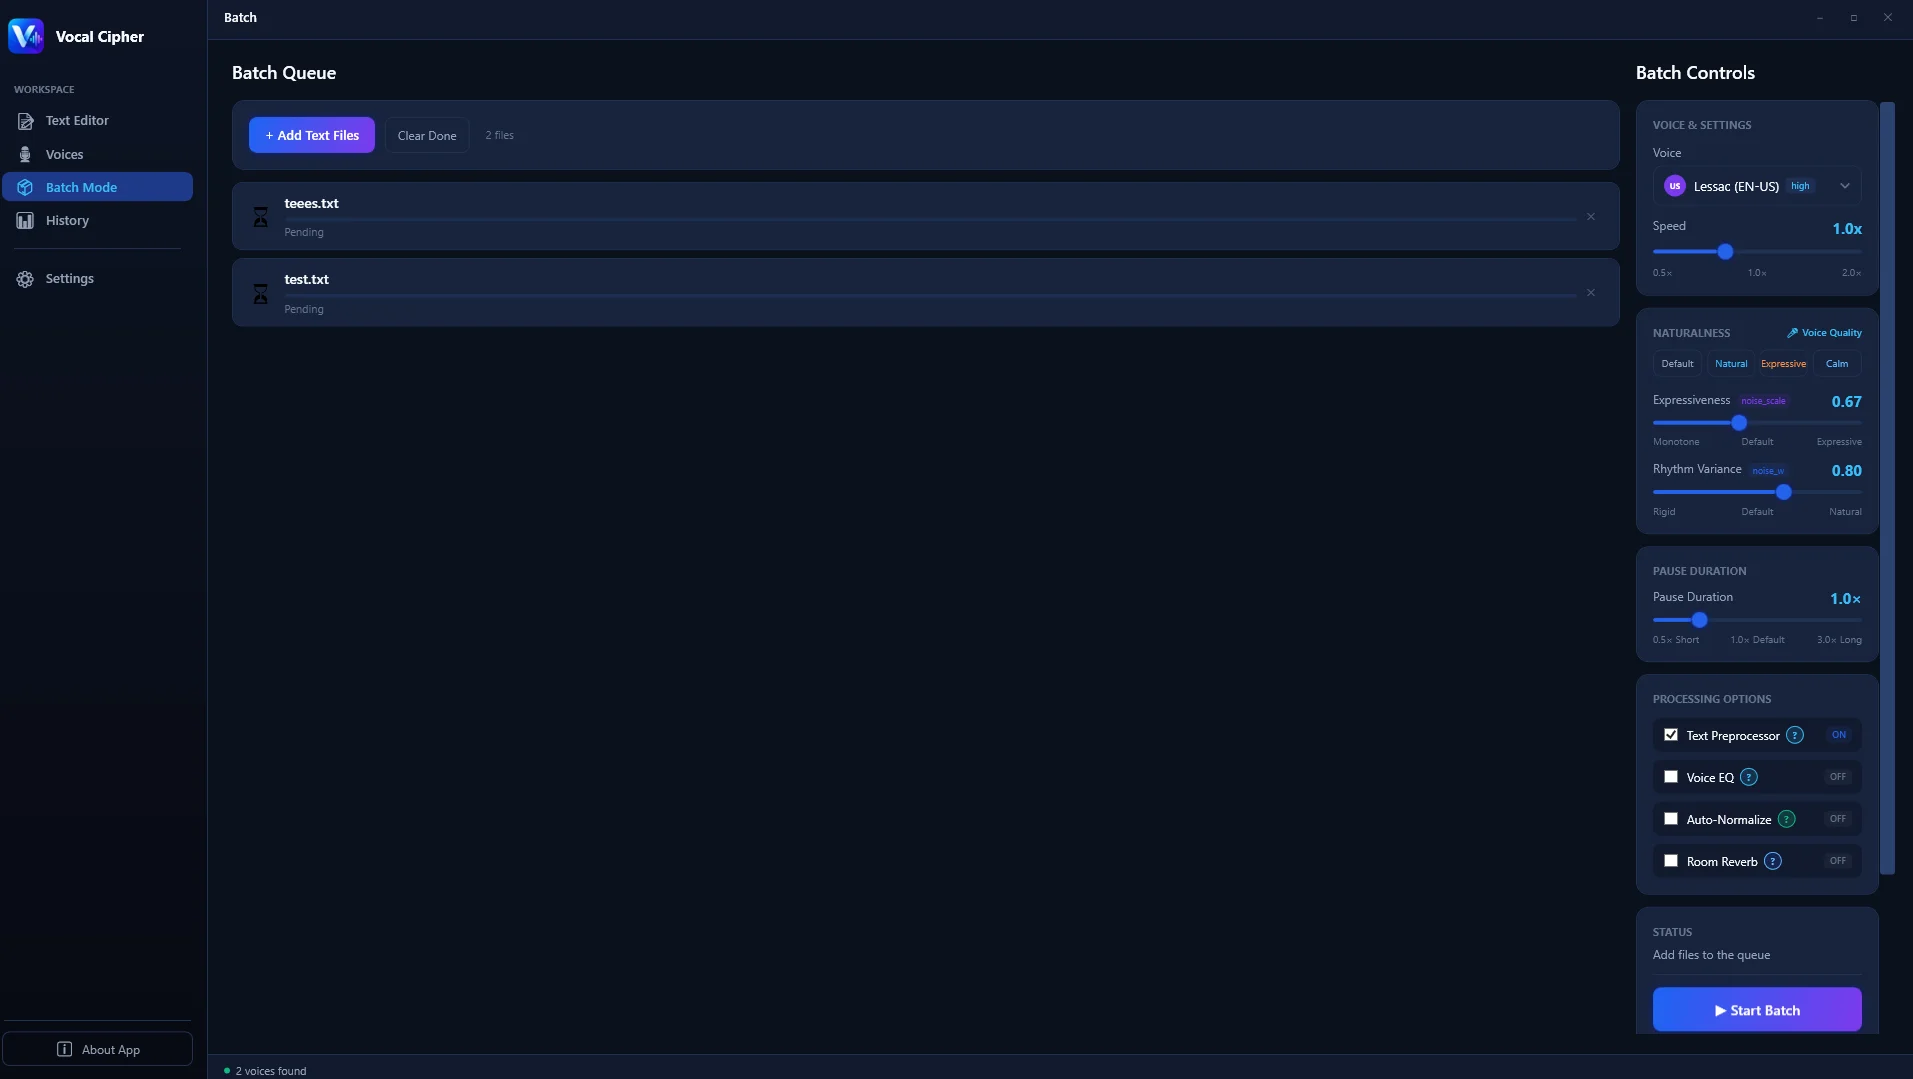
Process hundreds of confidential documents sequentially in a secure offline batch queue.
Enterprise Regulatory Compliance: HIPAA, GDPR, ITAR, and SOC 2
For regulated industries, the distinction between cloud and local speech synthesis is not a matter of convenience; it is a question of legal survival:
1. Healthcare & Pharmaceutical (HIPAA Compliance)
When healthcare institutions generate instructional audio for patient care plans, clinical trials, or psychiatric intake summaries, manuscripts frequently contain Protected Health Information (PHI). Uploading PHI to a cloud speech vendor without an executed Business Associate Agreement (BAA) triggers immediate federal HIPAA civil penalties reaching $50,000 per violation. Vocal Cipher keeps all patient data contained on local hospital hardware.
2. Defense & Aerospace (ITAR / CMMC Compliance)
Aerospace contractors producing narrated technical operating manuals for tactical flight simulators or defense hardware cannot transmit technical specifications outside the United States. Under International Traffic in Arms Regulations (ITAR) and Cybersecurity Maturity Model Certification (CMMC), cloud data transfers to commercial multi-tenant servers can constitute illegal defense technology export. Air-gapped local execution on Windows guarantees strict domestic hardware containment.
3. Entertainment & Gaming Industry NDAs
In the video game and film industries, leaking a single character death, plot twist, or celebrity voiceover role before an official announcement destroys tens of millions of dollars in marketing impact. Leading game development studios mandate that all dialogue prototyping must occur on air-gapped workstations behind physical studio badge access.
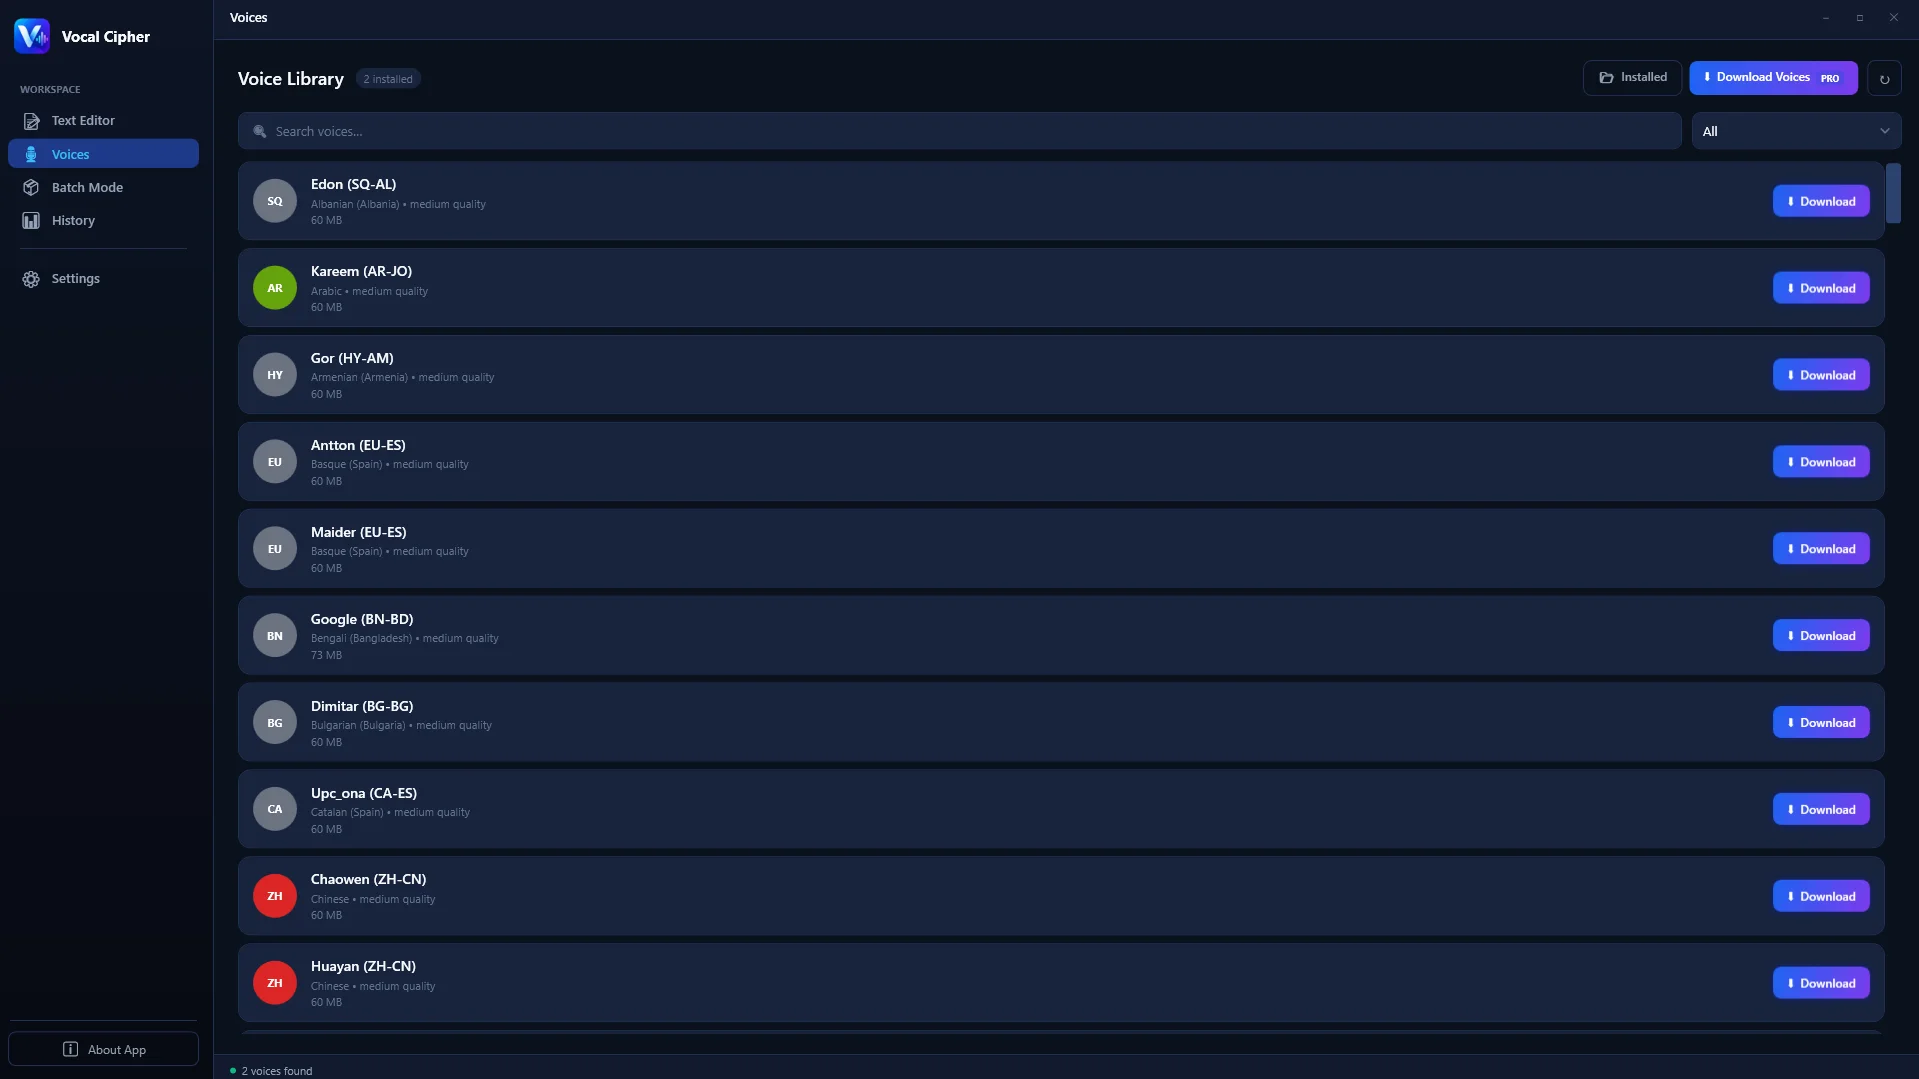
Audition dozens of distinct character voices locally without leaking creative intent to the cloud.
Comprehensive Security Architecture Comparison Matrix
Compare the physical security profiles of three primary voice generation architectures in 2026:
| Security Dimension | Public Cloud Voice API | Dedicated Cloud Instance | Vocal Cipher (Air-Gapped PC) |
|---|---|---|---|
| Physical Network Isolation | Zero (Public internet) | Partial (VPC tunnel) | 100% Total Physical Air Gap |
| Text Ingestion Logging | Logged in server diagnostics | Logged in cloud audit trail | Zero logging outside local RAM |
| Data Training Ingestion Risk | High (Subject to TOS) | Moderate (Contract dependent) | Zero (Mathematically impossible) |
| Compliance Overhead | Requires complex DPAs & BAAs | High enterprise cloud audits | Inherently compliant (Local boundary) |
| Internet Outage Resilience | 0% (Total operational failure) | 0% (Requires active connection) | 100% Permanent Autonomous Uptime |
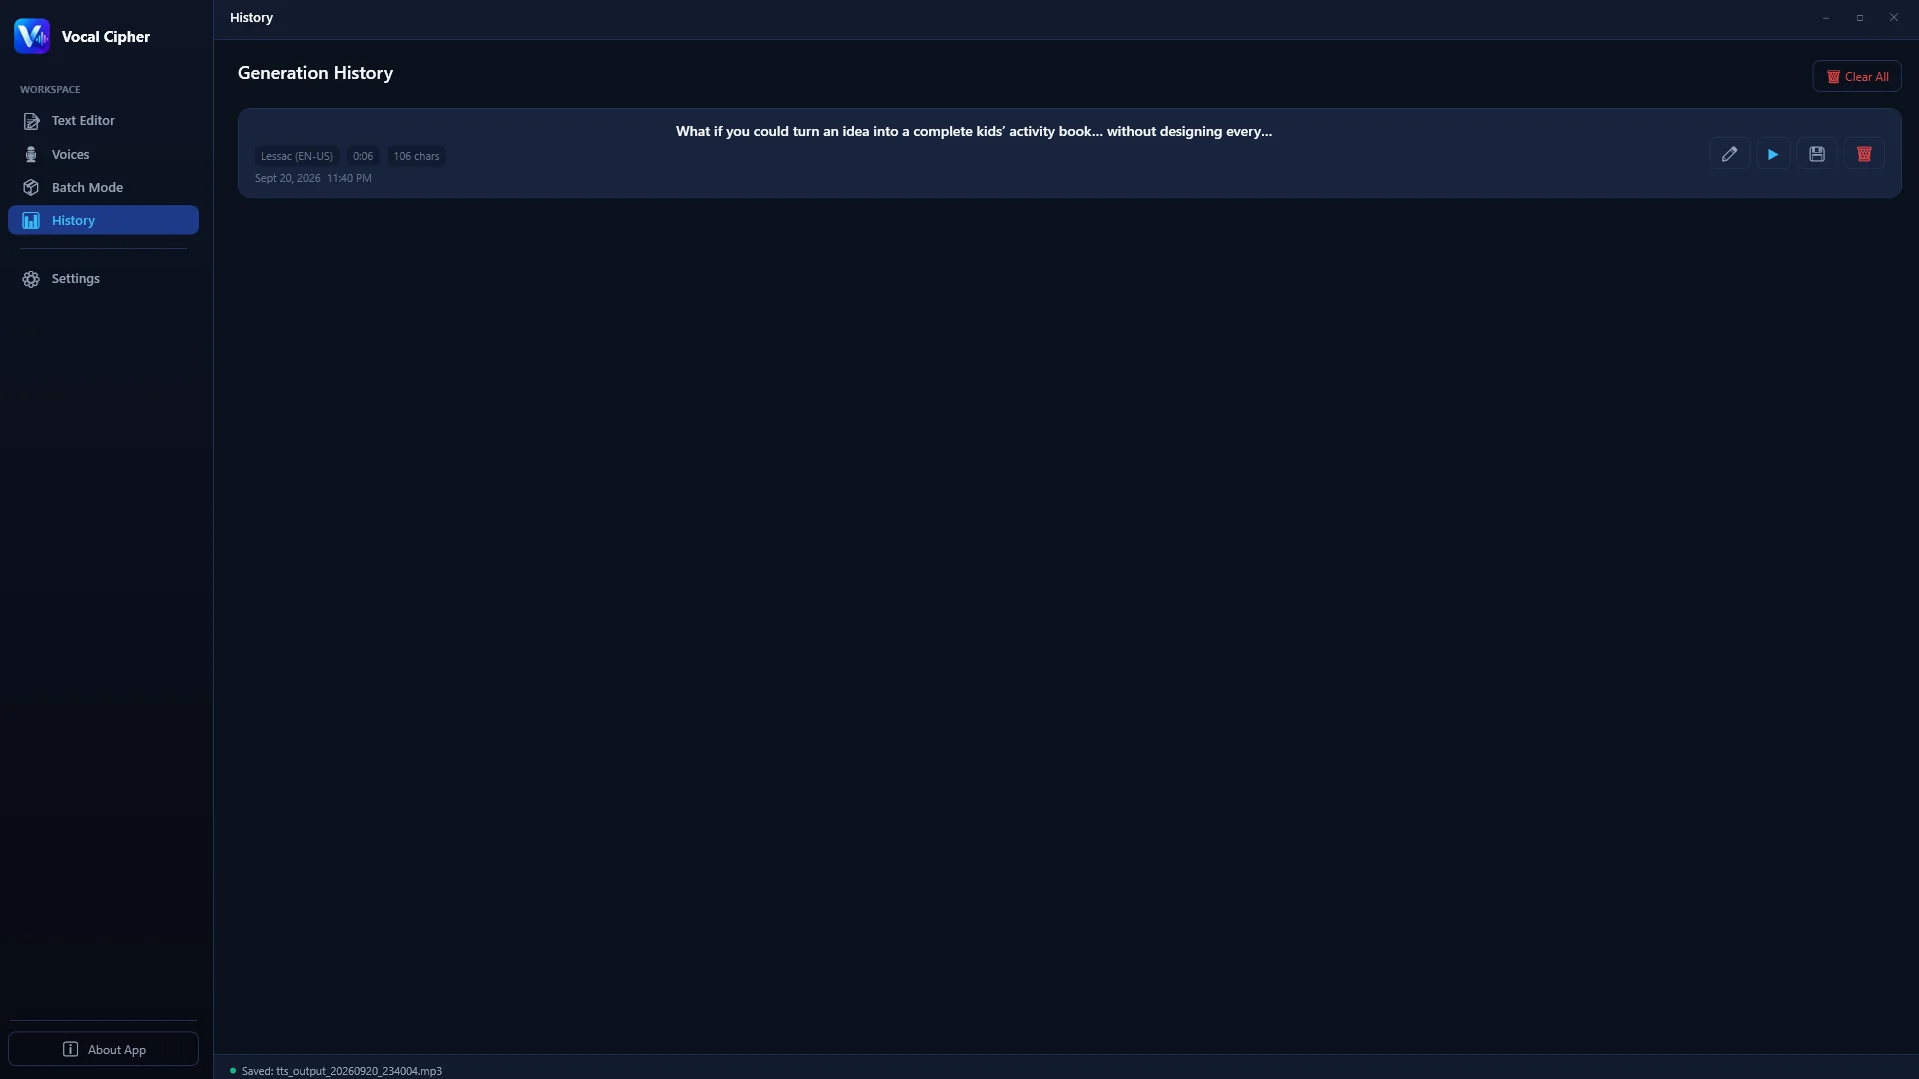
Rendered master WAV files remain strictly on your local encrypted storage partitions.
Step-by-Step Guide: Deploying Vocal Cipher on an Air-Gapped Windows Workstation
To establish an impenetrable, enterprise-grade voiceover workstation adhering to military and corporate isolation standards, follow this 4-step deployment procedure:
Physical Air-Gap Preparation
Disconnect the target Windows workstation from all Ethernet switches. In Windows Settings or Device Manager, disable Wi-Fi and Bluetooth wireless adapters, or disable wireless hardware entirely in the motherboard UEFI BIOS.
Transfer Installation Packages via Secure Media
Copy the self-contained Vocal Cipher installer and neural voice model packages onto a hardware-encrypted, write-blocked USB flash drive. Transfer the setup archive to the air-gapped machine and run the installer.
Local License Activation Verification
Launch Vocal Cipher. Enter your permanent desktop software license key. The software validates the cryptographic certificate locally against its embedded public key architecture without querying any external server.
Full Synthesis Operations in Complete Isolation
Begin drafting and rendering voiceovers. Paste top-secret scripts, adjust neural timbre parameters, and export uncompressed 24-bit WAV master stems straight to your encrypted BitLocker volume with absolute peace of mind.
Acoustic Excellence in Secure Environments: Why Air-Gapped Audio Sounds Better
A remarkable secondary benefit of local air-gapped speech synthesis is audio quality. Cloud platforms are constrained by streaming bandwidth economics; transmitting uncompressed 24-bit 48kHz audio across thousands of concurrent API requests requires massive cloud outbound data transfer bandwidth. Consequently, cloud providers quietly compress speech using lossy MP3 or Opus codecs before sending it to your browser.
Inside Vocal Cipher, synthesis happens directly between your GPU and local storage bus over PCIe lanes transferring at over 7,000 MB/s. Audio is written directly as uncompressed 24-bit 48,000Hz Linear PCM WAV files. There is zero downsampling, zero bit-rate throttling, and zero loss of high-frequency vocal formants or subtle room air.
Threat Modeling in Neural Voice Synthesis: 7 Cyber Attack Vectors on Cloud Speech APIs
When evaluating information security risks, enterprise CISOs must consider every vector through which confidential text and proprietary audio can be intercepted across cloud speech infrastructure:
- Vector 1: Corporate Egress Proxy Inspection: Enterprise TLS decryptors and security proxies intercept outbound employee web traffic. Any script pasted into a web browser is cached in intermediate firewall buffers.
- Vector 2: Cloud Storage Bucket Misconfigurations: Cloud voice platforms frequently store intermediate rendered audio in public or semi-private object storage buckets. Misconfigured S3 access control lists (ACLs) have repeatedly exposed millions of private audio recordings to public crawlers.
- Vector 3: Supply Chain Vendor Infiltration: A cloud voice startup may rely on dozens of third-party sub-processors for billing, logging, analytics, and infrastructure. A security compromise in any downstream sub-processor exposes customer scripts.
- Vector 4: Side-Channel Model Inversion Attacks: In shared cloud GPU environments, sophisticated adversarial tenants can execute cache timing attacks or model inversion queries to reconstruct training samples and text prompt embeddings from GPU memory buffers.
- Vector 5: Telemetry Packet Correlation: Even when payload encryption is enabled, network metadata (packet sizes, timing intervals, and endpoint IP routing) can be correlated by adversaries to deduce confidential corporate production schedules.
- Vector 6: Rogue Insider Data Exfiltration: Administrative personnel, systems operators, and customer support staff at third-party cloud hosting facilities possess privileged database access to user activity records and input text logs.
- Vector 7: Automated Training Pipeline Ingestion: Proprietary scripts uploaded to cloud endpoints are routinely ingested into unsupervised automated retraining datasets, causing future public foundation models to accidentally leak proprietary script fragments to external users.
The Zero-Trust Audio Pipeline: Architectural Blueprint for Secure On-Premises Voiceover
To achieve complete Zero-Trust compliance in creative audio production, security engineers implement a 4-layer containment architecture centered on Vocal Cipher:
| Security Layer | Implementation Protocol | Zero-Trust Protection Benefit |
|---|---|---|
| Hardware Boundary | Isolated workstation with disabled NICs | Zero physical pathway for packet escape |
| Storage Encryption | BitLocker AES-XTS 256-bit with TPM 2.0 | Protects voice models & scripts at rest |
| Execution Boundary | Direct PCIe DMA transfer to GPU VRAM | Bypasses shared multi-tenant memory |
| Media Egress Control | Hardware-authenticated storage keys only | Auditable physical custody of master WAV stems |
Case Study: How a Tier-1 Aerospace Contractor Eliminated ITAR Compliance Risk
In 2026, a major international aerospace manufacturer was tasked with producing 60 hours of technical audio narration for advanced avionics training simulators. The instructional scripts contained restricted technical data governed by International Traffic in Arms Regulations (ITAR) and Export Administration Regulations (EAR):
Aerospace Deployment Architecture
The Failure of Cloud 'Private VPC' Proposals
The contractor initially explored enterprise cloud voice APIs offering 'dedicated Virtual Private Cloud (VPC)' instances. However, corporate compliance auditors rejected the proposal: because foreign cloud engineers held administrative hypervisor access, transmitting technical data over the cloud was deemed an export control violation carrying potential multi-million-dollar fines.
The Air-Gapped Vocal Cipher Solution
The team installed Vocal Cipher on isolated, air-gapped Windows 11 workstations located inside physically guarded security vaults. Complete avionics flight manuals were ingested through the offline batch queue, synthesizing all 60 audio hours in under 4 business days.
The Results: Perfect Security and Uncompromised Speed
The project passed all defense security audits with zero findings. The contractor eliminated $18,000 in projected cloud API consumption costs, and the synthesized 24-bit 48kHz WAV audio stems were integrated directly into simulation software with pristine clarity.
Cryptographic Auditability: Verifying Zero Telemetry with Windows Sysinternals
Enterprise security leads do not rely on marketing promises; they verify binary behavior with forensic inspection tools. To prove that Vocal Cipher executes in complete digital silence, security teams can conduct a simple live audit on Windows:
- Launch Microsoft Sysinternals Process Monitor (Procmon): Set an inclusion filter for Process Name:
VocalCipher.exe. - Enable Network Activity Capture: Filter exclusively for network operations:
TCP Connect,TCP Send,UDP Send, andDNS Query. - Execute a 5,000-Word Speech Generation: Paste a large script into Vocal Cipher and click 'Synthesize'. Monitor Procmon in real time.
- Observe Zero Network Events: The network event log remains 100% empty. The software queries zero external domain names, binds zero listening sockets, and initiates zero remote API calls. All operations are strictly local file I/O and GPU direct memory access.
The Financial Exposure of Cloud Data Breaches vs. Air-Gapped Peace of Mind
According to annual enterprise cybersecurity audits conducted across the entertainment, technology, and defense sectors in 2026, the average global cost of an enterprise data breach exceeds $4.4 million. For content production studios and digital agencies, the damage is amplified by strict legal indemnification clauses:
- Contractual Breach Penalties: Standard Non-Disclosure Agreements for AAA video game titles and major motion pictures carry liquidated damage clauses ranging from $500,000 to over $5,000,000 if pre-release dialogue or story elements leak before public embargo dates.
- Catastrophic Client Churn: If an agency's cloud voice vendor suffers an unauthorized data exfiltration event that exposes client campaign assets, enterprise clients immediately terminate agency contracts and initiate breach-of-fiduciary lawsuits.
- The Air-Gapped Shield: By keeping all text processing and voice synthesis isolated on physical Windows hardware with Vocal Cipher, the likelihood of an external cloud exfiltration breach drops to mathematical zero.
Technical Checklist: Hardening Windows Workstations for Maximum Audio Synthesis Isolation
Enterprise security administrators preparing dedicated Windows audio editing suites for high-security clients should implement this comprehensive workstation hardening checklist:
- BIOS/UEFI Hardware Lockdown: Enter the motherboard UEFI firmware. Disable onboard Wi-Fi, Bluetooth controllers, and unused physical communication ports. Password-protect the BIOS to prevent unauthorized boot device selection.
- Windows Group Policy Network Restriction: Configure local Windows Group Policy Objects (GPO) to block outbound firewall connections on all profiles (Domain, Private, Public). Ensure no background operating system processes can broadcast telemetry pings.
- Dedicated BitLocker Partitions: Format the project audio storage drive using BitLocker AES-XTS 256-bit volume encryption. Store recovery keys in an offline hardware security module or corporate physical safe.
- Physical Ingress Auditing: Establish strict physical chain-of-custody protocols for any removable USB storage media utilized to transfer scripts or finished 24-bit WAV master stems into and out of the isolated editing suite.
Enforce Total Data Sovereignty with Vocal Cipher
Eliminate cloud data leaks, protect sensitive client NDAs, and generate studio-grade 24-bit voiceovers on air-gapped Windows workstations.
Get Vocal CipherFrequently Asked Questions (FAQ)
What exactly makes an AI voice generator 'air-gapped'?
An air-gapped system operates on a computer that has no physical or wireless network connection to the outside world. An air-gapped voice generator contains all required deep learning models and code locally, functioning autonomously without transmitting or receiving any data across external networks.
Does Vocal Cipher transmit any telemetry or usage metrics to external servers?
No. Vocal Cipher is engineered with zero telemetry. It does not track user sessions, word counts, script topics, or error logs across external servers. It runs in complete digital silence on your local machine.
Can government and defense contractors use Vocal Cipher for classified projects?
Yes. Because Vocal Cipher can be installed via physical media onto isolated workstations in Secure Compartmented Information Facilities (SCIFs) with disabled network hardware, it complies with strict CMMC and ITAR physical security boundaries.
How does local synthesis prevent intellectual property theft in creative industries?
By ensuring that unreleased scripts, dialogue, and narrative lore never leave your local encrypted NVMe storage drive, you eliminate the risk of third-party cloud data breaches, unauthorized employee access, and automated dataset scraping.
Can healthcare institutions narrate patient training guides without violating HIPAA?
Yes. Because no text or audio containing Protected Health Information (PHI) ever leaves the local clinical computer, healthcare providers avoid HIPAA cloud transfer liabilities and do not require third-party Business Associate Agreements.
Will Vocal Cipher expire or stop working if my PC stays offline permanently?
No. Vocal Cipher features permanent local licensing. It does not require periodic internet check-ins, hourly heartbeats, or cloud token refreshes to maintain full operational functionality.
Can I verify that Vocal Cipher is not making network connections using Windows tools?
Yes. Enterprise cybersecurity administrators can inspect Vocal Cipher using Windows Resource Monitor, TCPView, or Wireshark network protocol analyzers to verify that the application executable initiates zero outbound network connections.
Are there any word limits or monthly subscription fees when running offline?
No. Vocal Cipher operates with zero character meters, zero word limits, and zero monthly subscription fees. You retain unlimited synthesis capabilities on your Windows workstation.
How do enterprise IT teams distribute neural voice model updates to air-gapped workstations?
Voice models and software updates are packaged as standalone binary archives. System administrators can inspect, hash-verify (SHA-256), and virus-scan the packages on a secure staging terminal before transferring them via write-blocked, hardware-encrypted physical media directly onto the isolated air-gapped editing workstations.
Does running speech synthesis on an air-gapped PC interfere with DAWs like Pro Tools or Reaper?
No. Vocal Cipher is engineered for professional coexistence in digital audio workstations. Because GPU inference occurs in brief compute bursts and releases system memory immediately upon completion, audio editors can run Pro Tools, DaVinci Resolve Fairlight, or Adobe Audition alongside Vocal Cipher without audio buffer underruns, latency spikes, or sample dropouts.
Can multi-user creative teams share rendered voice assets across an isolated local network (LAN)?
Yes. Organizations can deploy an internal, closed-loop local area network (LAN) with zero gateway routing to the public internet. Editing suites can route their 24-bit WAV exports directly to an isolated on-premises Network Attached Storage (NAS) array, allowing multiple editors and sound designers to collaborate safely behind physical perimeter firewalls.
What measures prevent local memory dumps or pagefile residue from exposing sensitive scripts?
For high-security defense and enterprise environments, Windows administrators can enable the 'ClearPageFileAtShutdown' security policy and enforce full-disk BitLocker volume encryption. Vocal Cipher manages text buffers in volatile RAM and clears transient token structures immediately upon audio synthesis completion, ensuring that zero recoverable script fragments remain on physical drive platters or memory modules after system power-down.